Industry

Fintech Software Development

Ledger-accurate financial software with KYC/AML checks and PCI DSS-aligned payment flows built in from the schema up.

NDA on request · Free, no-obligation estimate · Reply within one business day

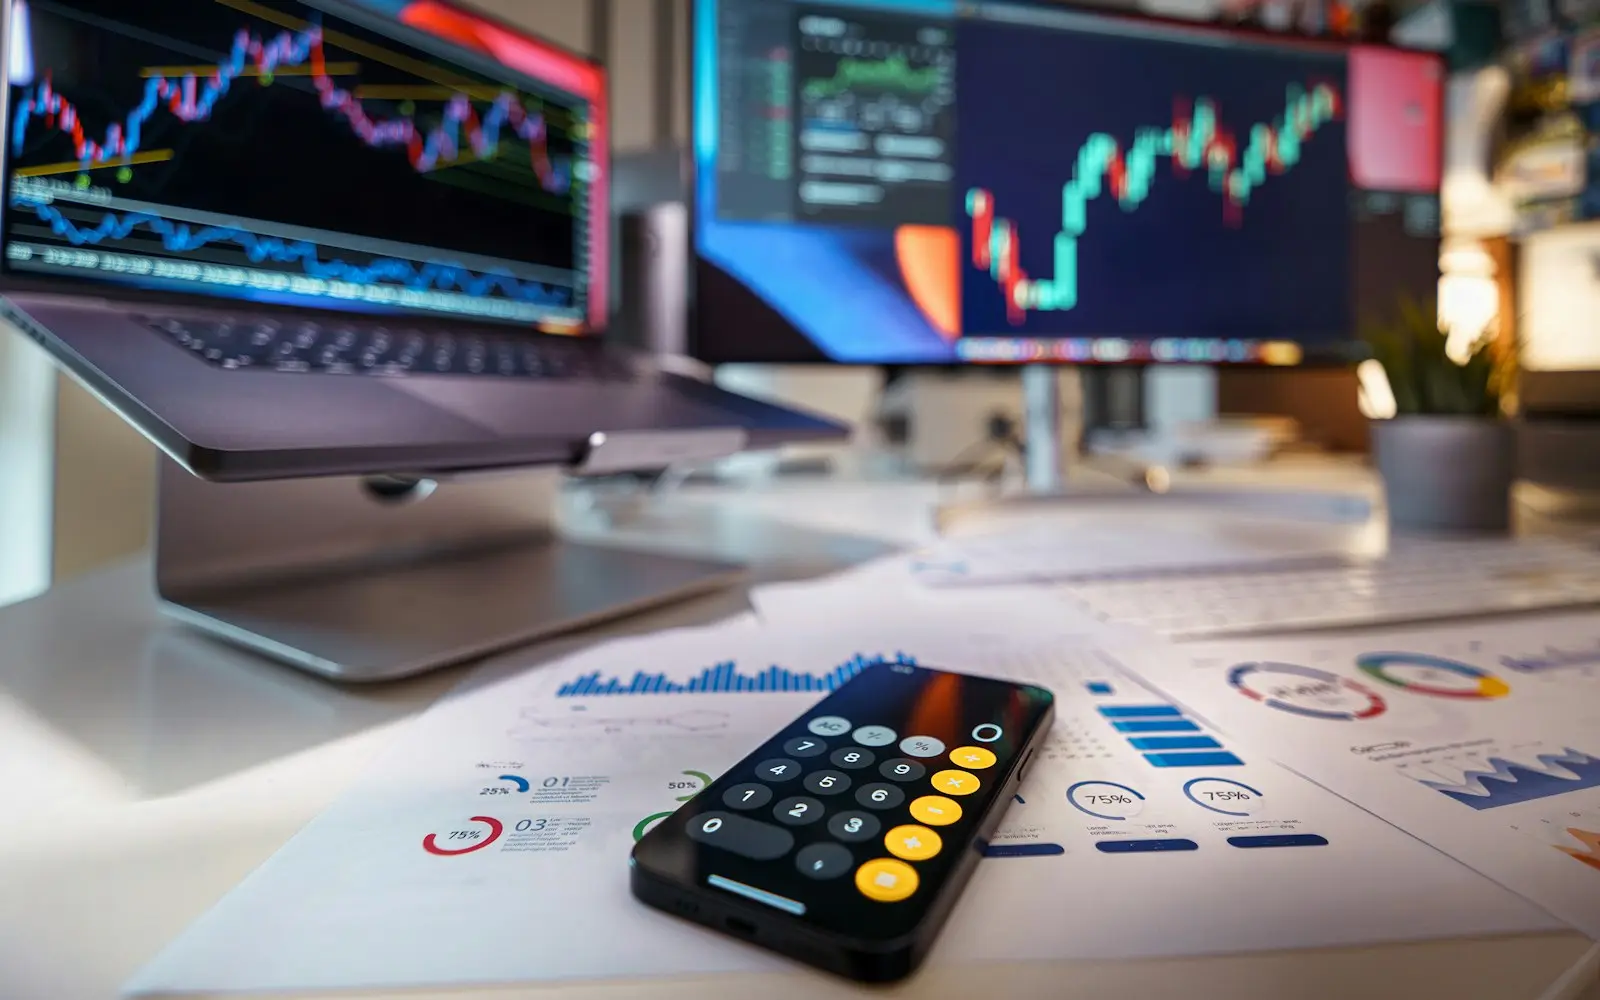
Desk with printed financial charts, a calculator and monitors showing market data
NDA before discovery
You own the code and IP on payment
Code in your repository from day one
A working demo every two weeks
Senior engineers do the work
How we work

Neobanks, lenders, payment platforms and wealth management tools all answer to the same standard: every cent has to reconcile, every new customer has to clear identity checks before money moves, and every card number has to stay out of scope for anyone who does not need to see it. Software that gets this wrong does not fail gracefully; it fails as a regulatory finding or a reconciliation gap that takes a finance team a week to trace.

We design the ledger, the KYC/AML onboarding flow and the payment integration together rather than as separate workstreams, using Plaid for account linking, Stripe or Adyen for processing, and identity providers like Persona or Alloy for verification and sanctions screening. Raw card data is tokenized at the edge so it never enters your application's PCI DSS scope.

Code lives in your repository from the first commit, and we scope infrastructure so a SOC 2 or PCI DSS audit has a real system to examine rather than a patchwork of after-the-fact controls.

The problem

Where fintech & banking software gets hard

  • Money has to reconcile to the cent

    A ledger that is off by a rounding error at scale becomes a finance team's full-time job. Double-entry accounting and idempotent transaction handling have to be correct from the first schema, not retrofitted once volume grows.

  • KYC and AML checks slow onboarding if bolted on

    Identity verification, sanctions screening and device fingerprinting each add friction. Done well, they run in parallel and route only genuine risk to manual review; done poorly, every applicant waits on a queue.

  • PCI DSS scope creeps into every screen that touches a card

    Any form field, log line or database column that stores a raw card number pulls that system into PCI DSS scope. Tokenization has to be designed in, not patched around a launch date.

  • Real-time payment rails leave no room to patch after the fact

    ACH, wire and instant payment rails settle in seconds to minutes. An error caught after submission means a support ticket and a manual reversal, because payment rails offer no rollback.

  • Regulatory reporting changes faster than the roadmap

    SAR filing thresholds, state money transmitter licensing and cross-border settlement rules shift independently of your release calendar, so reporting logic needs to be config-driven rather than hardcoded.

What we build

Fintech & Banking systems we build

  • Ledger and reconciliation systems

    A double-entry ledger with immutable transaction history, matched automatically against processor and bank settlement files so discrepancies surface the same day, not at month-end close.

  • KYC and AML onboarding flows

    Tiered identity verification, sanctions and PEP screening, and ongoing transaction monitoring built around providers like Persona, Alloy or ComplyAdvantage, with a manual review queue for genuine edge cases only.

  • Payment integrations

    Bank account linking through Plaid, card and alternative payment processing through Stripe or Adyen, and settlement logic that models partial failures as first-class states with their own handling.

  • Card issuing and spend controls

    Program management, real-time authorization rules and spend limits built on issuing platforms like Marqeta, wired into your ledger so every authorization has a matching entry.

  • Fraud detection and risk scoring

    Rule-based and model-based risk scoring at signup and at transaction time, tuned to your actual fraud patterns instead of a generic threshold that blocks legitimate customers.

  • Mobile and web banking applications

    Account dashboards, transfers and statements built against the same ledger and KYC services as your back office, so the app never shows a balance the ledger cannot back.

  • Regulatory reporting tooling

    SAR and CTR generation, audit exports and licensing recordkeeping built as configurable rules, so a threshold change is a settings update rather than a code release.

Regulations and standards we design for

  • PCI DSS scope reduction through tokenization for any flow that touches card data, keeping raw PAN storage out of your application entirely.
  • KYC and AML program requirements under the Bank Secrecy Act, including customer identification, sanctions screening and suspicious activity monitoring.
  • Software architecture designed to support a SOC 2 Type II audit, with access logging and change control built in rather than assembled before the audit window.
  • PSD2 strong customer authentication for platforms processing card payments from EU cardholders.
  • GLBA Safeguards Rule requirements for handling nonpublic personal financial information.
  • State money transmitter licensing recordkeeping, including transaction logs and ledger retention periods that examiners can request.

Platforms we integrate with

  • Plaid for bank account linking and balance verification
  • Stripe and Adyen for card and alternative payment processing
  • Marqeta for card issuing and real-time authorization controls
  • Persona and Alloy for identity verification and KYC/AML orchestration
  • Dwolla and the ACH network for bank transfers
  • SWIFT and correspondent banking rails for cross-border settlement
  • Visa and Mastercard network tokenization for stored payment methods

Ledger design that survives a reconciliation audit

We build the ledger as an append-only, double-entry system: every transaction posts as balanced debit and credit entries, and nothing gets deleted or edited after the fact, only reversed with a new entry. Idempotency keys on every payment request prevent a retried API call from posting the same transfer twice, which is where most young fintech ledgers first go wrong.

A daily reconciliation job compares your ledger balance against the processor's settlement file and the bank's actual balance, flagging drift the same day rather than at month-end. When a payment fails partway through (authorized but not captured, or captured but not settled), the ledger models that as a distinct state instead of forcing it into 'pending' until someone investigates manually.
KYC and AML onboarding that does not lose every third signup

We split verification into tiers: a light check (document scan, basic sanctions screening) clears most signups in under a minute, while enhanced due diligence, higher transaction limits or a PEP match routes to a manual review queue with the applicant's evidence already assembled.

Ongoing monitoring runs as a background process against transaction patterns, not just at onboarding, since AML obligations do not end once an account opens. SAR-eligible activity gets flagged with the supporting transaction history attached, so your compliance team is reviewing a case file, not reconstructing one from raw logs.

Keeping PCI DSS scope small on purpose

The cheapest way to pass a PCI DSS assessment is to never hold card data in the first place. We route card capture through the processor's hosted fields or tokenization vault so a card number never reaches your servers, which drops most of the application out of PCI scope and turns a full assessment into a much shorter self-assessment questionnaire.

FAQ

Fintech & Banking software FAQs

How long does it take to build a KYC/AML onboarding flow?

A working onboarding flow with document verification and sanctions screening typically takes eight to twelve weeks. Timeline grows if you need enhanced due diligence tiers, ongoing transaction monitoring, or integration with more than one identity provider for redundancy.

Do we need PCI DSS compliance in place before you start building?

No. We design the payment flow to route card data through tokenized, processor-hosted fields from the start, which reduces your PCI DSS scope to a self-assessment questionnaire in most cases. The compliance assessment itself is something your organization completes, not something we certify on your behalf.

Can you integrate with Plaid for bank account verification?

Yes. We use Plaid for account linking, balance and identity verification, and transaction history retrieval, and we design fallback handling for when a user's bank is not supported or a Plaid Link session expires mid-flow.

What is the practical difference between KYC and AML in the product?

KYC verifies who a customer is at onboarding, through document checks and identity matching. AML is ongoing: transaction monitoring, sanctions list rechecking and suspicious activity reporting that continues for the life of the account, not just at signup.

How do you handle ledger reconciliation when a payment fails mid-transaction?

The ledger models authorization, capture and settlement as distinct states rather than a single pending flag. A payment that authorizes but never captures reverses automatically after the processor's timeout window, and every state change writes its own ledger entry so support staff can see exactly where a transaction stalled.

Do you build card issuing programs or only payment acceptance?

Both. For issuing, we integrate with platforms like Marqeta to handle card creation, real-time authorization rules and spend controls, wired into the same ledger used for payment acceptance so every card transaction has a matching, reconciled entry.

Talk to us about your fintech & banking project

Share a few details about your project. A senior engineer reviews every request and replies with next steps, questions, and a rough budget range.

Get a free project estimate