Oceania

Software Development Company in Australia

A remote development team for Australian buyers, working to the Privacy Act, the Notifiable Data Breaches scheme and the payment methods Australian customers expect.

NDA on request · Free, no-obligation estimate · Reply within one business day

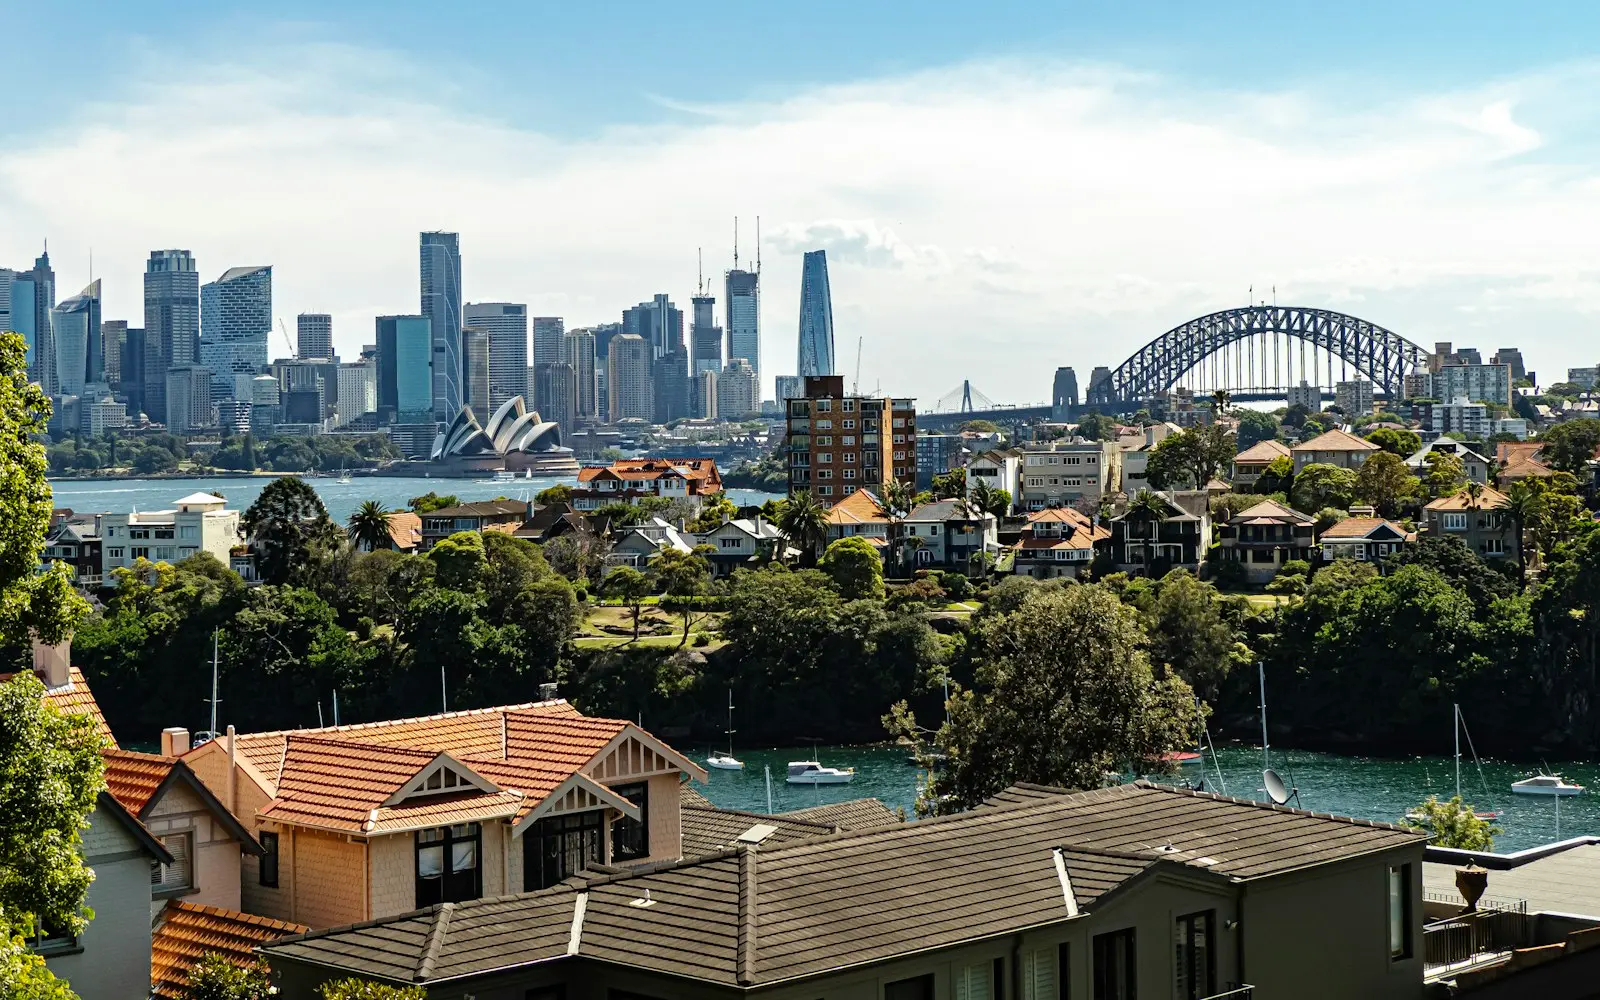
Sydney skyline and Harbour Bridge viewed across the harbour on a sunny day
NDA before discovery
You own the code and IP on payment
Code in your repository from day one
A working demo every two weeks
Senior engineers do the work
How we work

We build software for Australian companies as a remote team, with delivery cycles set to overlap AEST or AEDT business hours and specs and recordings kept as the source of truth for stakeholders who join outside them. There is no local office to visit; the value is in a team that already understands the rules an Australian buyer has to answer to.

That means designing around the Privacy Act 1988 and the Australian Privacy Principles from the first data model, planning for the Notifiable Data Breaches scheme's reporting obligations, and building in the payment rails and shipping integrations Australian customers actually use rather than the ones common in the US or UK.

Privacy obligations shape the data model, not just the policy page

The Australian Privacy Principles under the Privacy Act 1988 govern how personal information is collected, stored, used and disclosed, and the Notifiable Data Breaches scheme requires reporting eligible breaches to affected individuals and the regulator. We build access logging, encryption at rest and breach-detection hooks into the architecture at the start, because retrofitting them after a system is live is slower and more expensive than planning for them upfront.
Open banking changes what a fintech-adjacent product can request

The Consumer Data Right lets an Australian customer authorize secure data sharing between accredited providers, most visibly in banking. A product that wants to pull transaction data or account details needs to work within CDR's accreditation and consent model rather than screen-scraping or ad hoc integrations. We scope CDR-compliant data access early in projects that touch financial data.

A three-hour spread inside one country

Sydney and Perth run up to three hours apart, and the eastern states shift for daylight saving while Western Australia does not. We fix standing meetings to a window that holds for both, and treat async updates and recorded walkthroughs as standard practice rather than a fallback.

  • Standups scheduled to hold across AEST/AEDT and AWST
  • Written specs and recorded demos for stakeholders outside the meeting window
  • Support and release windows agreed up front, not assumed

Compliance

Regulations we design for in Australia

  • Privacy Act 1988 and the Australian Privacy Principles

    Sets the rules for collecting, storing, using and disclosing personal information. We design consent capture, data minimization and access controls around the APPs from the first data model rather than adding them during a security review.

  • Notifiable Data Breaches scheme

    Requires organizations to report eligible data breaches to affected individuals and the Office of the Australian Information Commissioner. We build logging and incident-detection capability into systems so a breach can be identified and reported inside the scheme's timelines.

  • Consumer Data Right

    Governs consent-based data sharing in banking and, over time, other sectors. Products that request or expose financial data are built to work within CDR's accreditation and consent flows rather than around them.

  • Spam Act 2003

    Requires consent before sending commercial electronic messages, plus a functional unsubscribe mechanism. We build opt-in capture and suppression lists into any system that sends marketing or transactional email or SMS.

  • WCAG accessibility expectations

    Australian government and enterprise buyers commonly expect WCAG 2.2 conformance for public-facing systems. We build to those standards as part of development rather than as a separate remediation pass.

Working together

Contracts, invoicing and working hours

  • AUD invoicing

    Contracts and invoices are issued in Australian dollars against agreed delivery milestones.

  • Overlap across AEST, AEDT and AWST

    We agree a standing meeting window that works for your team whether it sits in Brisbane, Melbourne or Perth, and keep specs and recordings available so daylight-saving shifts do not disrupt delivery.

  • Local payment and delivery integrations

    For commerce-facing builds we integrate BPAY, PayID and Afterpay alongside card payments, and connect to Australia Post or Sendle for shipping, rather than assuming payment methods common in other markets.

  • Contracts and IP

    We sign an NDA before discovery, code lives in a repository you control from the first commit, and IP assigns to you on payment.

FAQ

Frequently asked questions

Do you need an Australian entity to build software for us under the Privacy Act?

No. The Privacy Act and the Australian Privacy Principles govern how the system you commission handles personal information, not where the development team is based. We design consent capture, storage and access logging to meet those obligations and deliver the work remotely.

What does the Notifiable Data Breaches scheme mean for a system you build for us?

It means the system needs the logging and monitoring to detect a breach and support your reporting obligations to affected individuals and the regulator inside the scheme's timelines. We build that capability into the architecture rather than treating breach response as a manual afterthought.

Can you integrate Afterpay and PayID into an e-commerce or mobile checkout?

Yes. Afterpay, PayID and BPAY are standard checkout options for Australian buyers, alongside card payments, and we integrate whichever combination matches your customer base and risk appetite.

How does the Consumer Data Right affect a fintech product we're building?

If the product requests or shares banking data, it needs to operate within CDR's accreditation and consent framework rather than through direct scraping or informal data-sharing arrangements. We scope that requirement early so it shapes the architecture instead of forcing a rebuild later.

How do you handle collaboration across Australia's time zones, including Perth?

We set standing ceremonies to a window that holds across AEST, AEDT and AWST, which shift relative to each other during daylight saving, and rely on written specs and recorded demos so Perth-based stakeholders are never the last to know a decision.

Do you handle GST on software built for us?

GST treatment of software and imported digital services is a tax question for your accountant, not something we advise on. What we can do is build invoicing and checkout systems that display tax correctly once you've confirmed the applicable treatment.

Start a project with a team that plans around your working hours

Share a few details about your project. A senior engineer reviews every request and replies with next steps, questions, and a rough budget range.

Get a free project estimate